Incident Response
Notification lists after a breach
Post-breach data review to identify affected individuals and their information, delivered as a validated, de-duplicated notification list.
The challenge
After a data breach, you must work out who was affected, and quickly.
Identified across the affected data
One record per individual
List in your counsel's format
Scope that keeps counsel in control
How modern teams approach incident response
Notification deadlines after a breach can be measured in days. Before counsel can notify anyone, someone must find every individual in the compromised data, identify what information was exposed and reconcile duplicates across files.
We review the affected data to identify individuals and the personal information involved, then de-duplicate and validate the results into a clean notification list in the format your counsel needs. Our scope is focused: we prepare the list, and your counsel drafts and sends the notifications.
Review affected data
Documents reviewed to identify individuals and the information involved.
A clean notification list
De-duplicated, validated and in the format your counsel needs.
A focused scope
We prepare the list. Your counsel drafts and sends the notifications.
Go slow to go fast
We prove the approach on a small sample with you first, then scale. Here is how the work flows, and where AI carries the load versus where our attorneys apply judgement.
Technology where it adds value
An indicative view of how work is shared between AI and our attorneys at each stage. Judgement, protocol and sign-off always stay with people.
- 01
Receive data
10% 90%Affected data received securely and scoped.
- 02
Identify people and data
65% 35%Individuals and exposed data elements identified.
- 03
Validate and de-duplicate
45% 55%Records reconciled into one entry per individual.
- 04
Deliver the list
10% 90%Validated notification list delivered to counsel.
What you receive
A validated notification list your counsel can act on.
Where it fits best
- Ransomware and data exfiltration events
- Business email compromise
- Lost or exposed file shares
- Vendor-side breaches
Pricing that fits the shape of the work
The attorney who scopes your work shares pricing up front. These are the models that typically suit incident response.
Fixed fee
Best for
Defined projects, such as a CLM assessment or a contract clean-up.
How it is billed
One price for an agreed scope and outcome.
Unit rate with cap
Best for
Variable volume, such as document review or abstraction.
How it is billed
Per document or per contract, with a ceiling on total spend.
Managed team
Best for
Ongoing work, such as platform operations or monitoring.
How it is billed
A monthly fee for a dedicated team, scaled up or down with notice.
Hybrid
Best for
Programmes that mix a project with steady run work.
How it is billed
A fixed fee to build, then a unit rate or team fee to run.
What clients ask us
No. We prepare the validated list; your counsel drafts and sends the notifications.
Related services
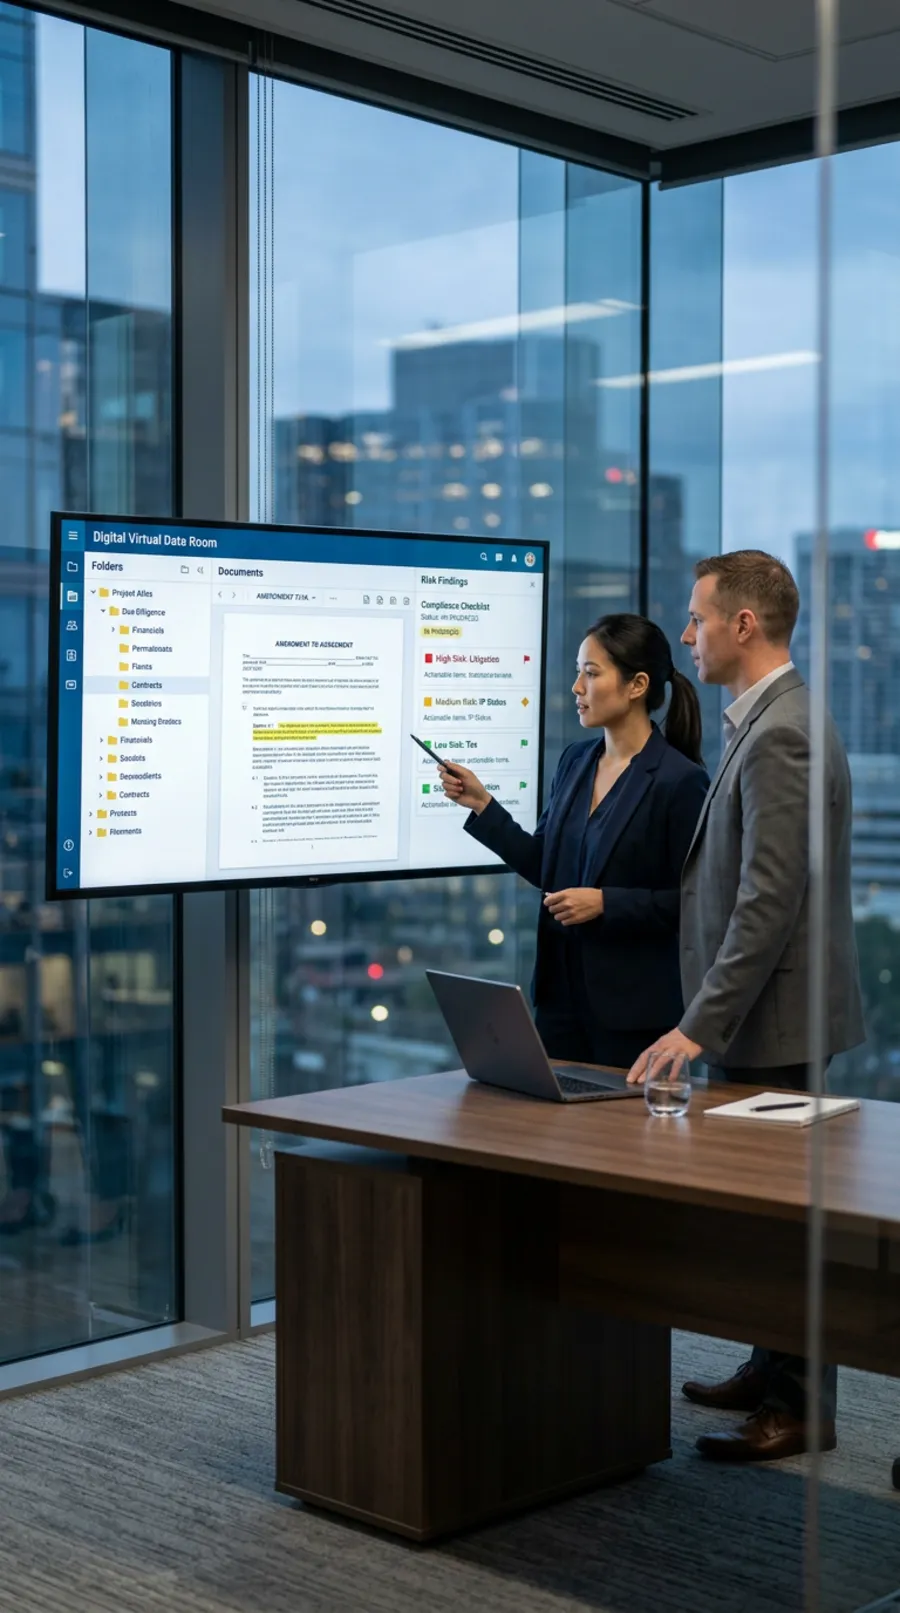
Due Diligence
Rules-based document review for any diligence exercise, from M&A and vendor onboarding to regulatory change, with findings, gaps and exposures extracted and checked by reviewers.
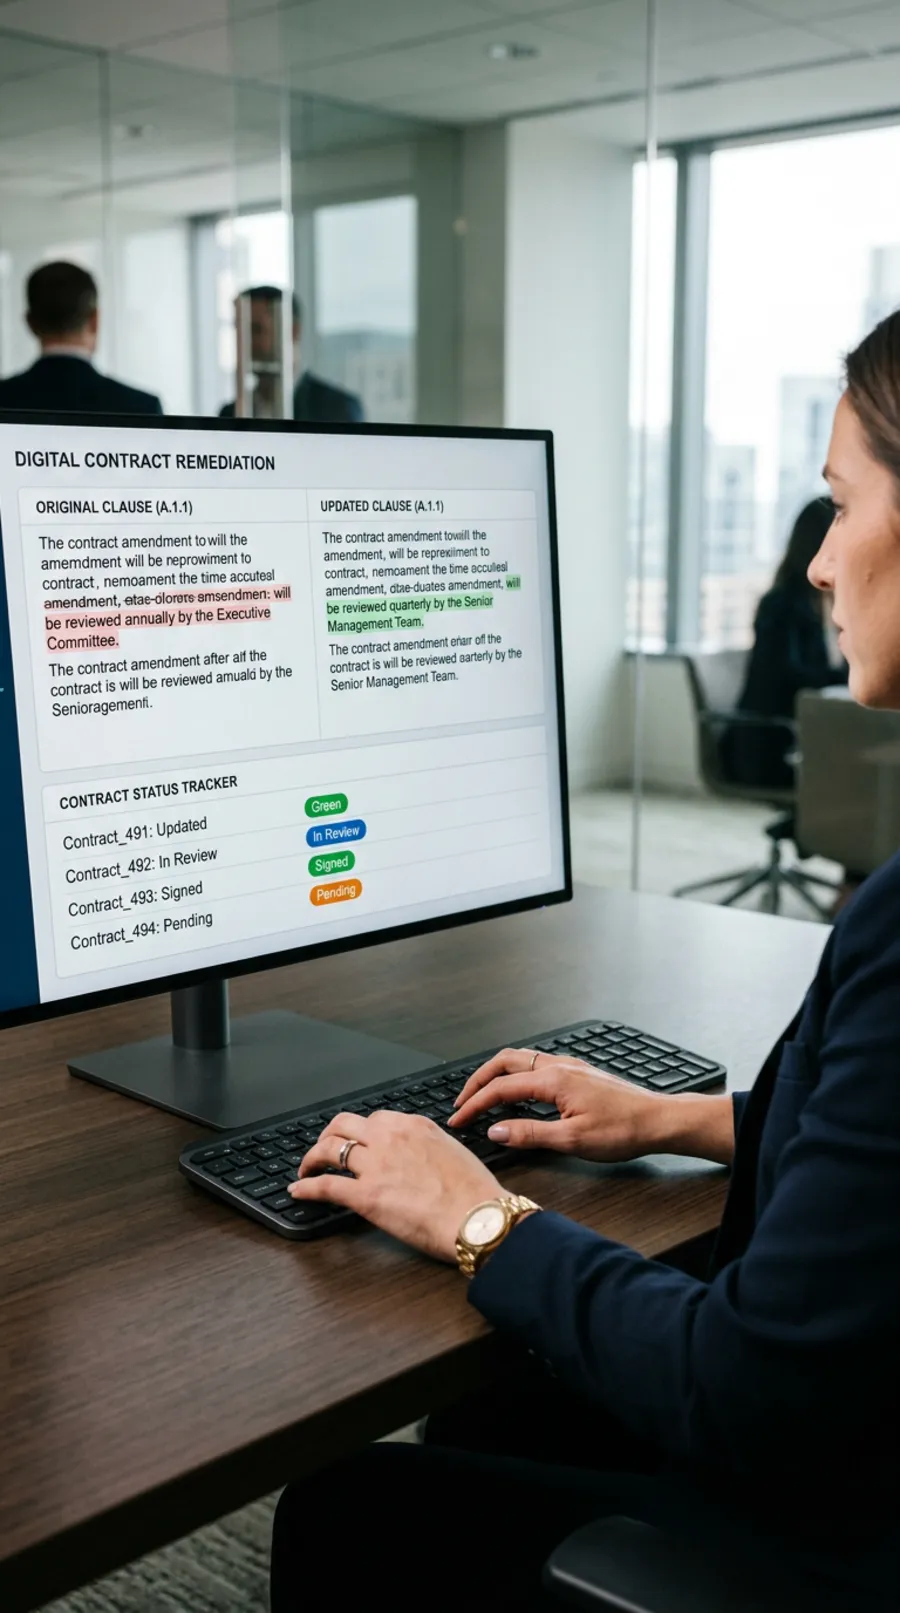
Contract Remediation
Counsel-guided repapering of live contracts after a regulatory, policy or business change, scaled to the deadline with a live status tracker.
Regulatory Survey
Validated multi-jurisdiction legal research, compared side by side, as a one-time report or continuous monitoring of change.
KYC
Sector-agnostic know-your-customer screening and documentation using your tools or online data sources, with consistent records for every entity.
Data Subject Access Requests
GDPR-focused DSAR support: collected data reviewed to find what relates to the requester, with third-party and confidential information redacted.
Move from breach to notification with clarity
We review the affected data, identify every impacted individual and deliver a validated, de-duplicated notification list you can rely on.
Start a Conversation